
Extremely well organized and high value
The course is extremely well organized and the pace is also very conducive to the learning process. The exercises are very well organized. Delivered very high value.

Cisco
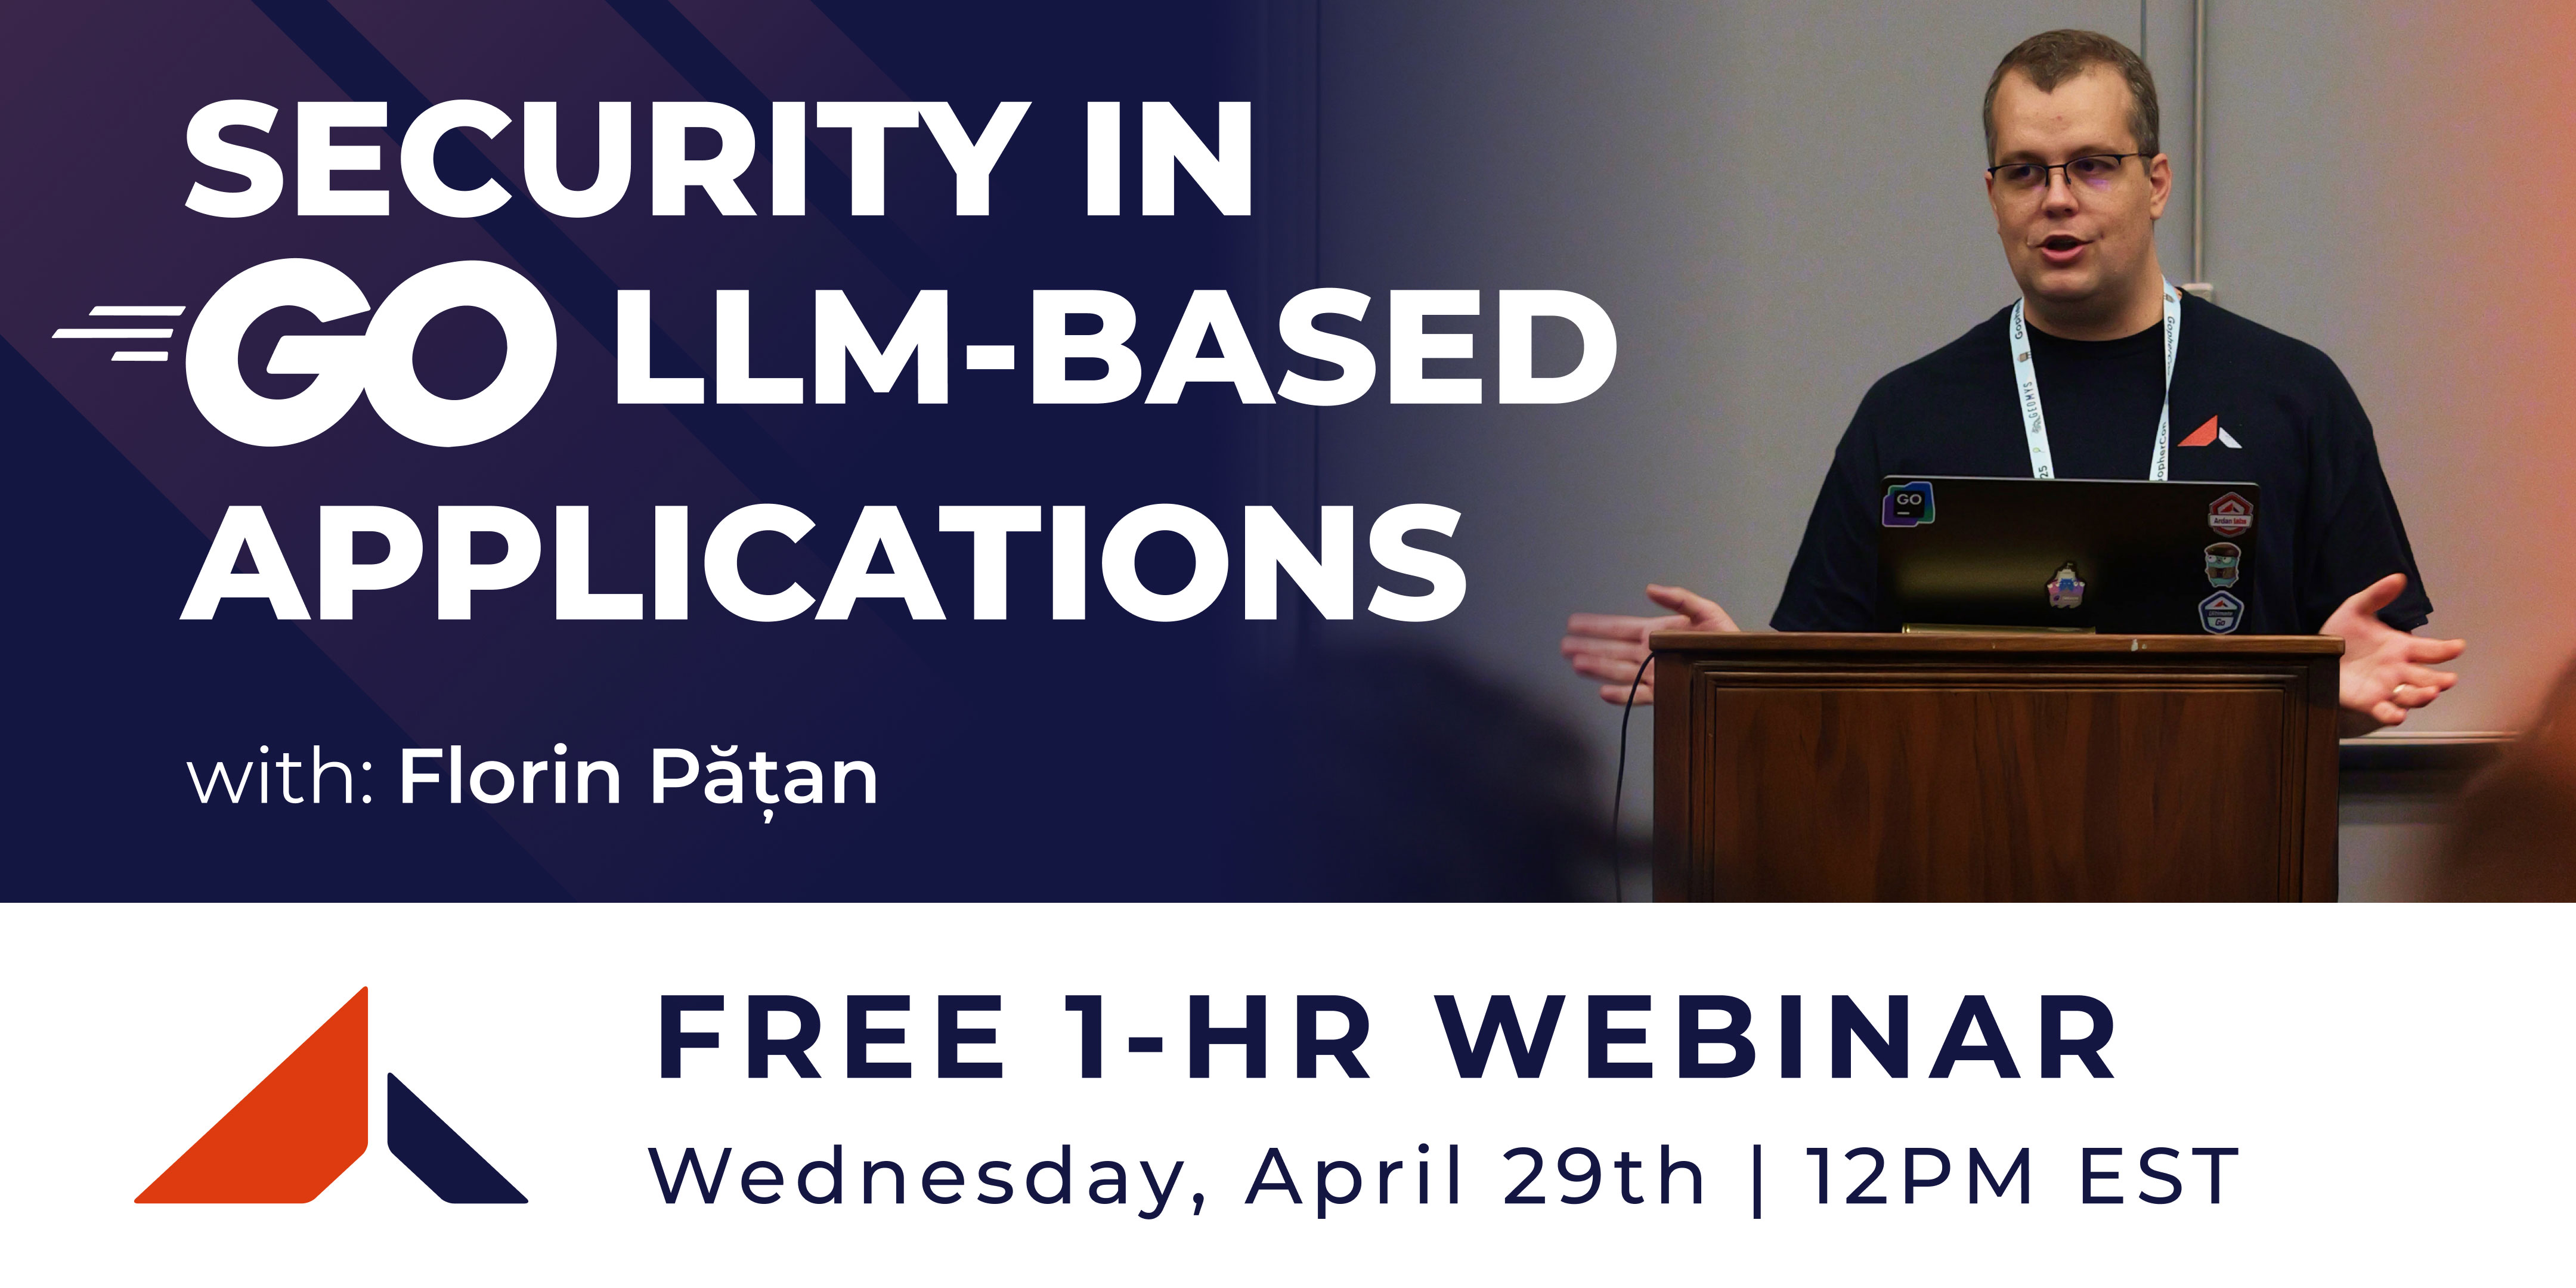
Apr 29th, 2026
12:00PM - 1:00PM EDT
Remote
Secure Go-LLM apps: learn to block prompt injection, secure tool calls via least-privilege, and stop RAG data poisoning with robust patterns.
Free:
Enroll NowSecure Go-LLM apps: Learn to block prompt injection, secure tool calls via least-privilege, and stop RAG data poisoning with robust patterns
As more Go applications use LLMs in one way or another, security is more important than ever.
In this talk, we’ll explore some design patterns to keep your application secured against a range of attacks, such as:
Join us to explore this critical area and learn together how to write safer applications.
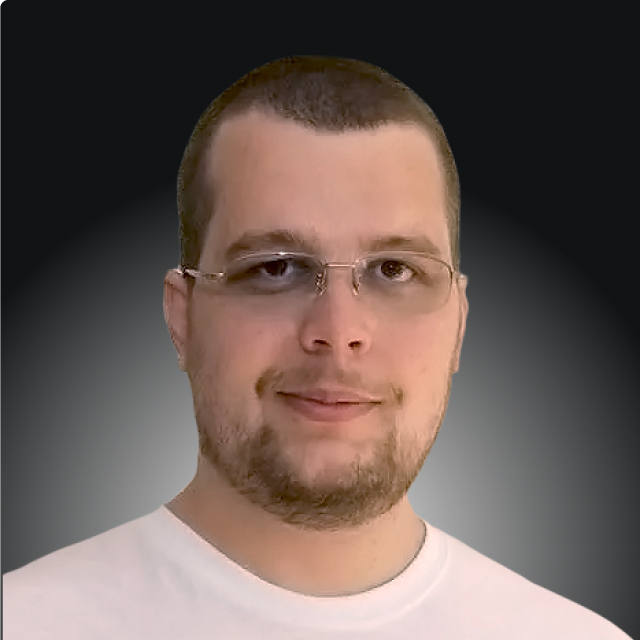
Instructor
Senior Engineer / Go Instructor
Florin has been working with Go daily for over a decade. He was involved in shaping GoLand, the Go IDE from JetBrains, and has consulted several high-profile clients with Ardan Labs. Florin is actively engaged in AI development and builds resilient systems that help people worldwide.

Have a team of 5+ engineers that can benefit from our courses? We have a business account for you.
Let's TalkThe course is extremely well organized and the pace is also very conducive to the learning process. The exercises are very well organized. Delivered very high value.
Cisco
You should reach out to the team over at Ardan Labs. They have been training the Go community since the beginning and I've yet to see anyone do it better.

Kelsey Hightower
Feeling so happy with myself: yesterday at work I refactored some code to use Go 1.16 built-in embed. I learned about it at an Ardan Labs service class.

Jessica Greene
Excellent class. The instructor is a hacker speaking to hackers, so we got very useful information and advice. Well-structured and paced. 10/10 would gopher it again.

ZipRecruiter
I finished Ultimate Service from Ardan Labs. I'm telling you this was the best ever. Talking from project structures to metrics. Now I can write good services in Go.

Adeniyi Oluwatola
Thanks Ardan Labs for a great Ultimate Go class! Bill is a great teacher and I'm definitely more productive in Go now.

Steve Francia
Highly recommend Ultimate Go by Bill Kennedy and Ardan Labs. I appreciate how Bill explains complex topics simply and clearly. The labs were incredibly helpful too.

Matt Holt
Their quality is astounding. They went above and beyond what we asked, working in line with best practices. Everything had test cases, was well documented and well structured, and ran smoothly.

Cole Calistra
ArdanLabs was the perfect partner for us because there is no better Go training out there and their engineer augmentation services didn't feel like engaging with contractors. Their engineers are true team players and great mentors for our team.

Tradesy
Great class! Our teams benefited from post-class help in code reviews, mentoring, and development of starter kits for typical applications types in our environment.

PayPal
The folks at Ardan Labs undertook all the tasks around software delivery (continuous integration, continuous delivery, unit testing, documentation, system integration) with the same commitment to quality that they demonstrated towards their code.

Carnegie Technologies
Absolutely professional delivery of content. Engaging, to the point, great exercises, and very well rehearsed. You can tell Miki Tebeka is passionate about what he does.
GoodRx
Where ideas get tested and shared. From the Lab is your inside look at the tools, thinking, and tech powering our work in Go, Rust, and Kubernetes. Discover our technical blogs, engineering insights, and YouTube videos created to support the developer community.
Explore our content:
Updated on
Miki Tebeka
Updated on

Ardan Labs

Jul 30, 2025 | Watch AI Agents with Kenneth Stott

Ardan Labs